Detection shouldn’t depend on where you store.
7AI Federated SIEM connects your security sources, including the SIEM and security data lake you already run, and runs detection against them wherever they live. Keep your logs where it makes sense, and reach them for detection, search, and enrichment.
However you want to work
You decide where your data lives.
Most teams run detection in more than one place, and the seams are where things get missed. Detection has always been tied to storage, so every decision about where data lands quietly becomes a decision that shapes what your detection can reach.
A federated approach works with what you already run. Keep your SIEM and connect it as a source. Move high-volume logs into a security data lake. Or run fully federated. Detection is abstracted from storage, so the same detection logic runs across every source, wherever it sits, so you maintain one set of rules. Here’s what it looks like in practice.
01 / Detections on All of It
Write the rule once. Run it where the data is.
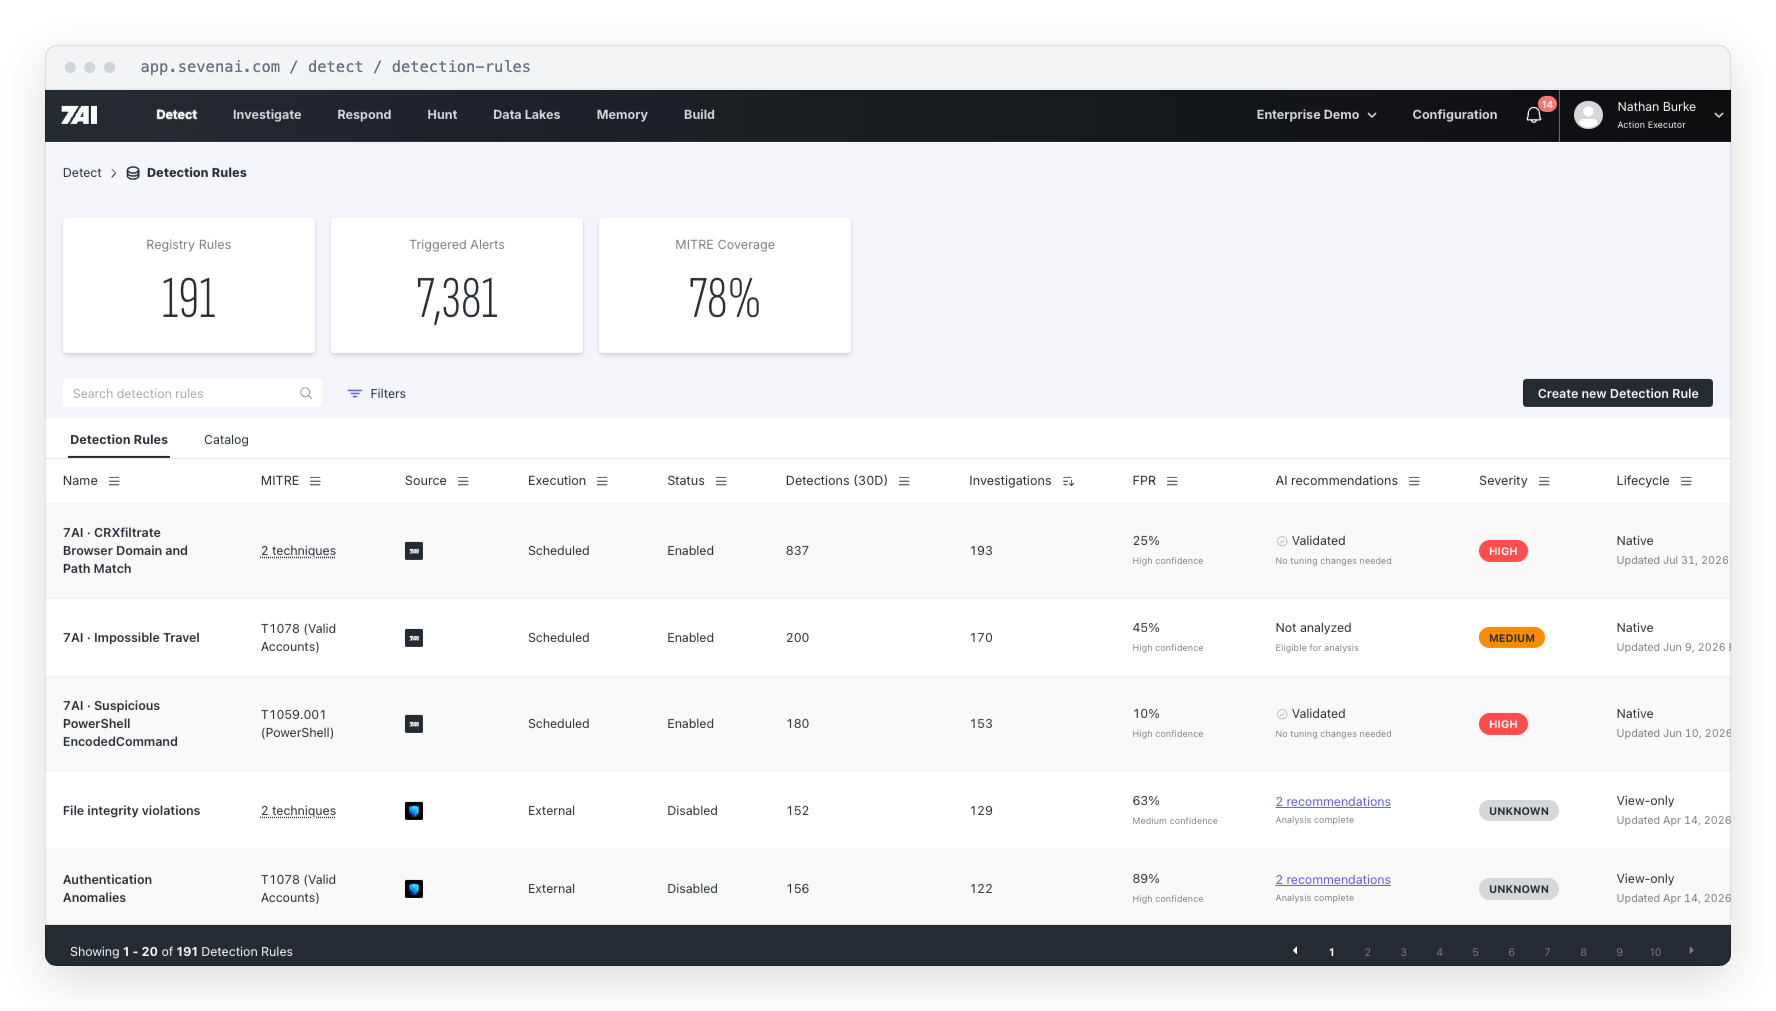
7AI runs detection rules against your connected log sources in two ways. On sources 7AI collects, rules evaluate events as they arrive. On sources you keep yourself, rules run as scheduled queries against the data in place. Same rule, written once. 7AI autonomous agents analyze the rules you’re running, flag thin coverage or noisy rules, and recommend changes with the reasoning behind each one.
- Consolidated detection engine to see every rule you’re running and where it applies.
- Rules mapped to MITRE ATT&CK.
- Draft a rule straight from a federated search.
02 / Your Logs, Your Way
Keep what you want, where you want.
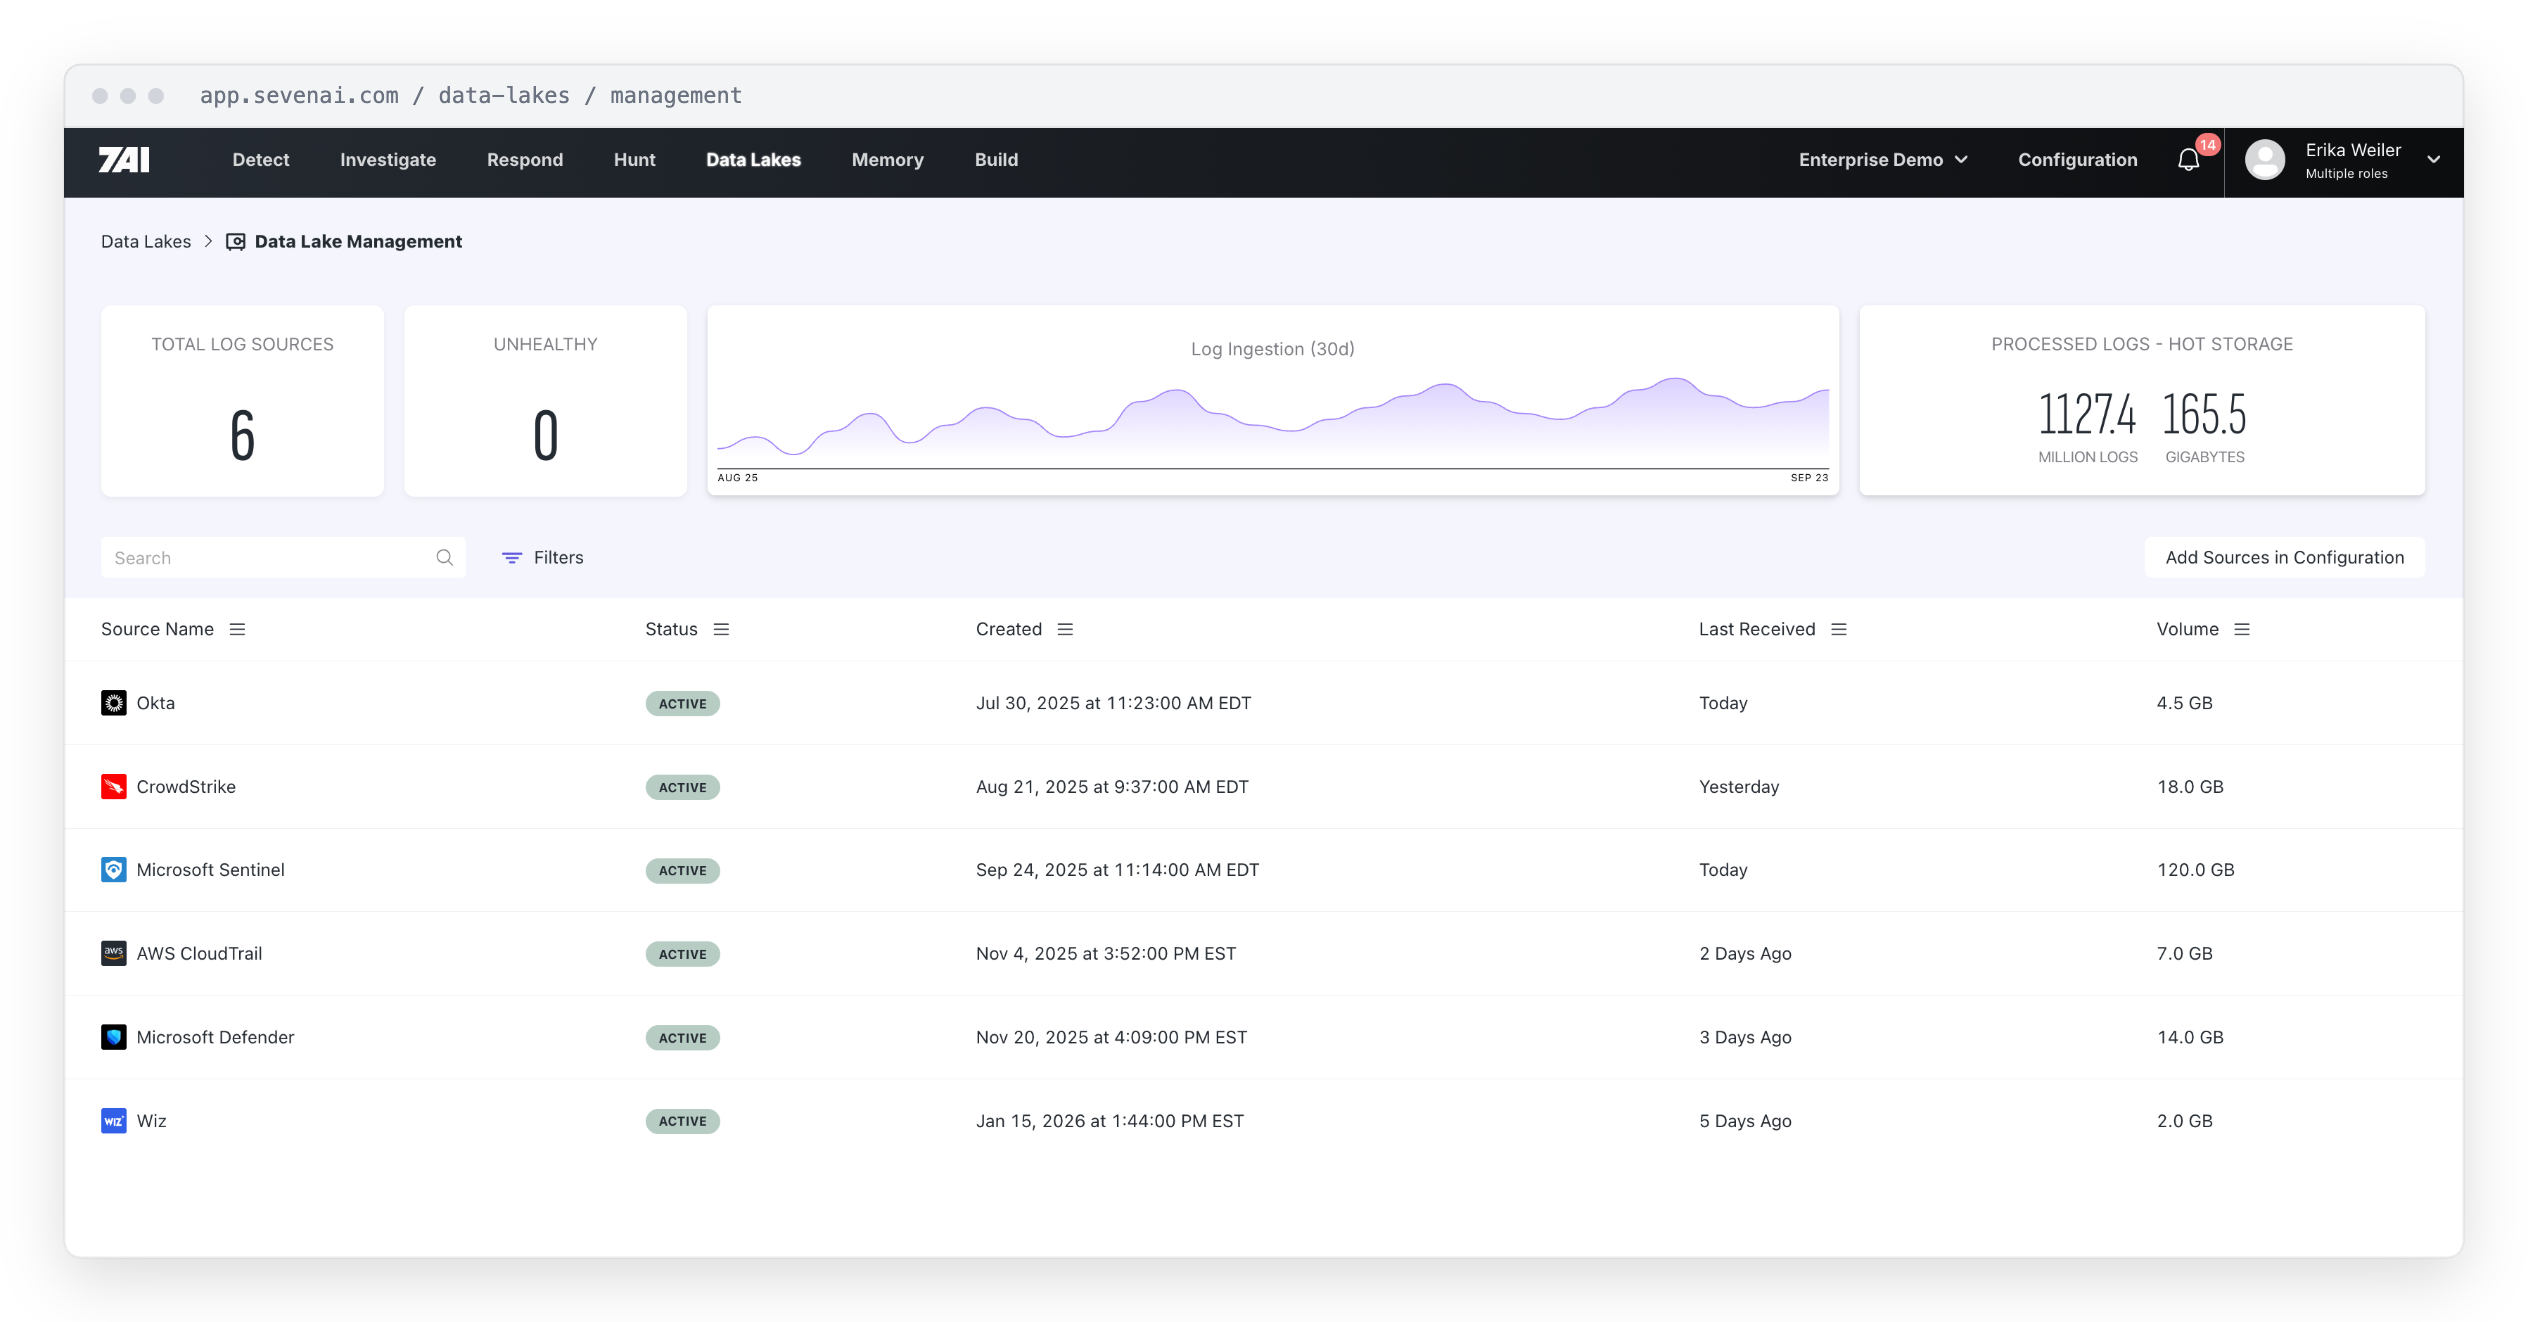
Let 7AI collect and store your log sources so it’s one connected system. Retention for as long as your policy requires, and rules that evaluate events continuously as they arrive
- Retain logs in 7AI, your existing SIEM, your security data lake, or a mix.
- Detection on ingest wherever 7AI collects.
- Health and volume monitoring for every source 7AI ingests.
03 / Search Across Everything
Ask in plain language, answer from your connected sources.
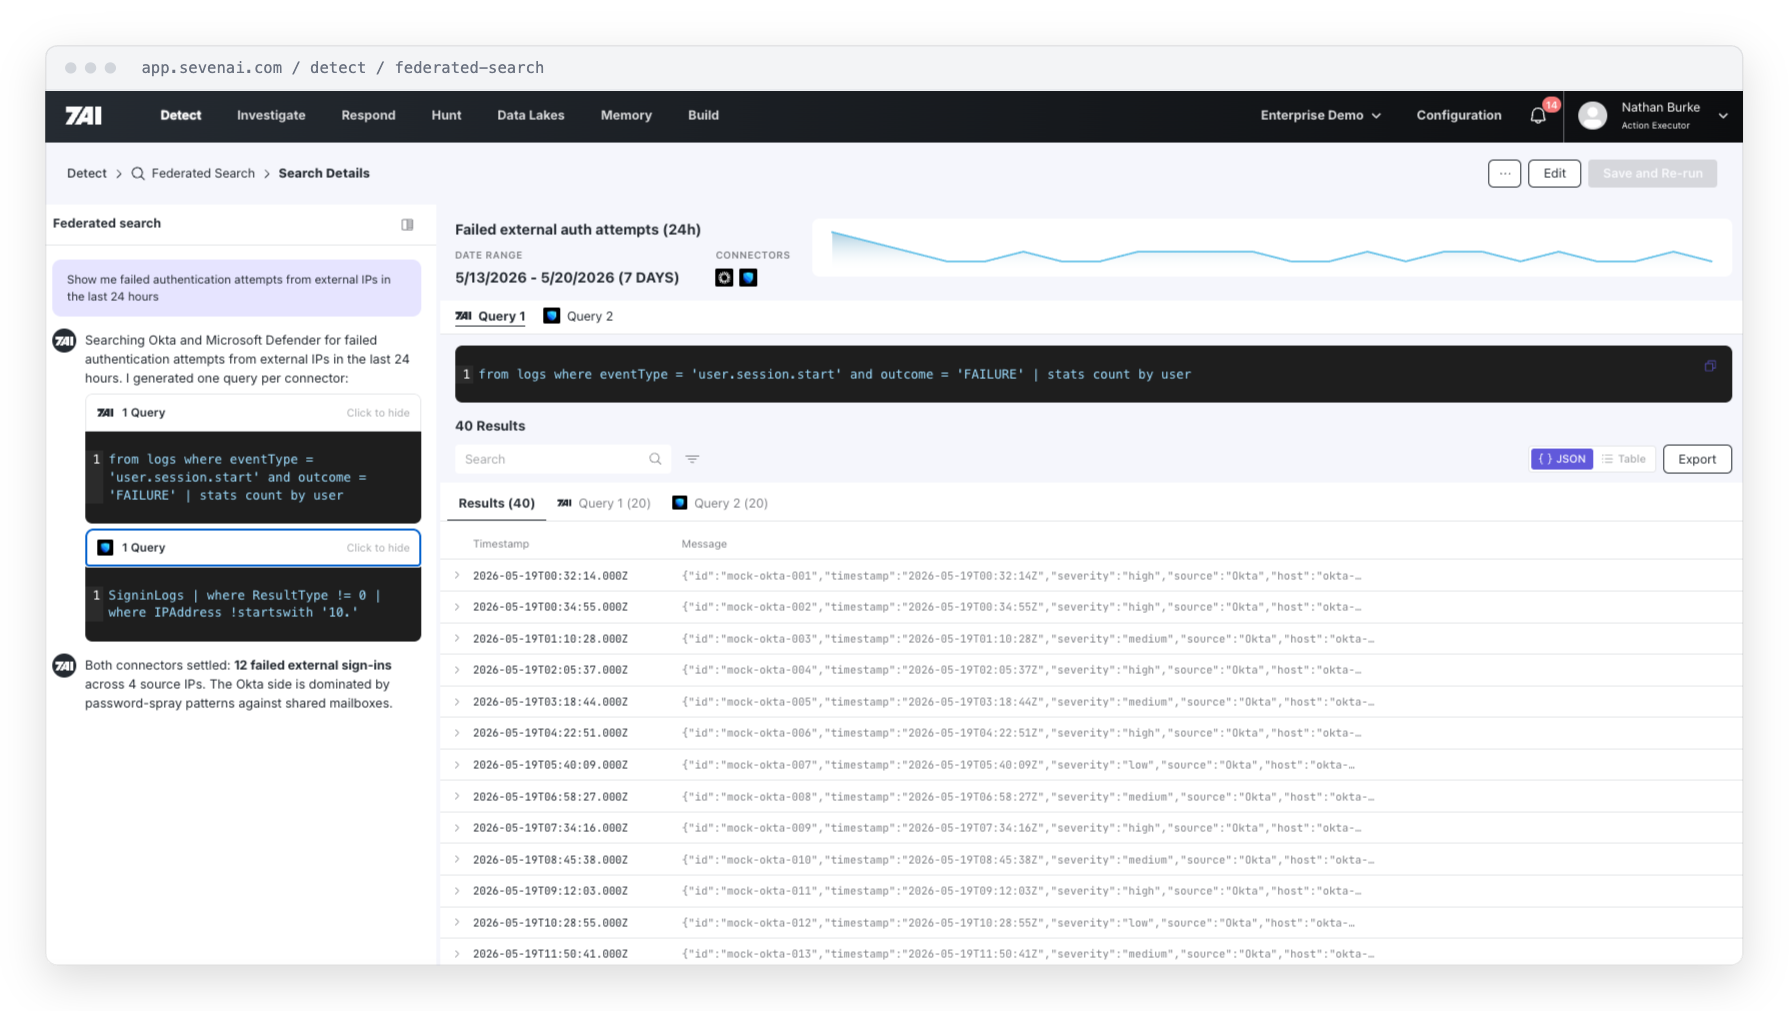
Federated Search queries your connected log sources and returns results normalized to OCSF, so fields line up across sources instead of arriving in four different shapes. Ask in natural-language and refine as you go.
- Natural-language search across every connected source.
- Results normalized to OCSF, so every source shares the same fields.
- Export to CSV, or draft a detection from any search.
Questions
Federated SIEM, answered.
Federated SIEM is the data foundation on which the rest of the platform runs, feeding detection, investigation, response, and threat hunting.
Take the full tour
See Federated SIEM on your sources.
We will walk you through federated search, log management, and detections across your own sources, including the SIEM you already run.