Your detection stack, continuously optimized.
7AI connects every detection source you run, maps your coverage to the techniques attackers actually use, finds the rules drowning your team in false positives, and routes each detection to the right outcome. With humans on the loop.
The problem with detection
A louder detection stack is not a safer one.
Every tool you add produces more alerts, more overlap, and more noise, and real threats hide inside it. Most teams have no single view of what their detections are catching, where coverage is thin, or which rules are generating false positives. 7AI gives you that view, and keeps it sharp.
01 / Detection Intelligence
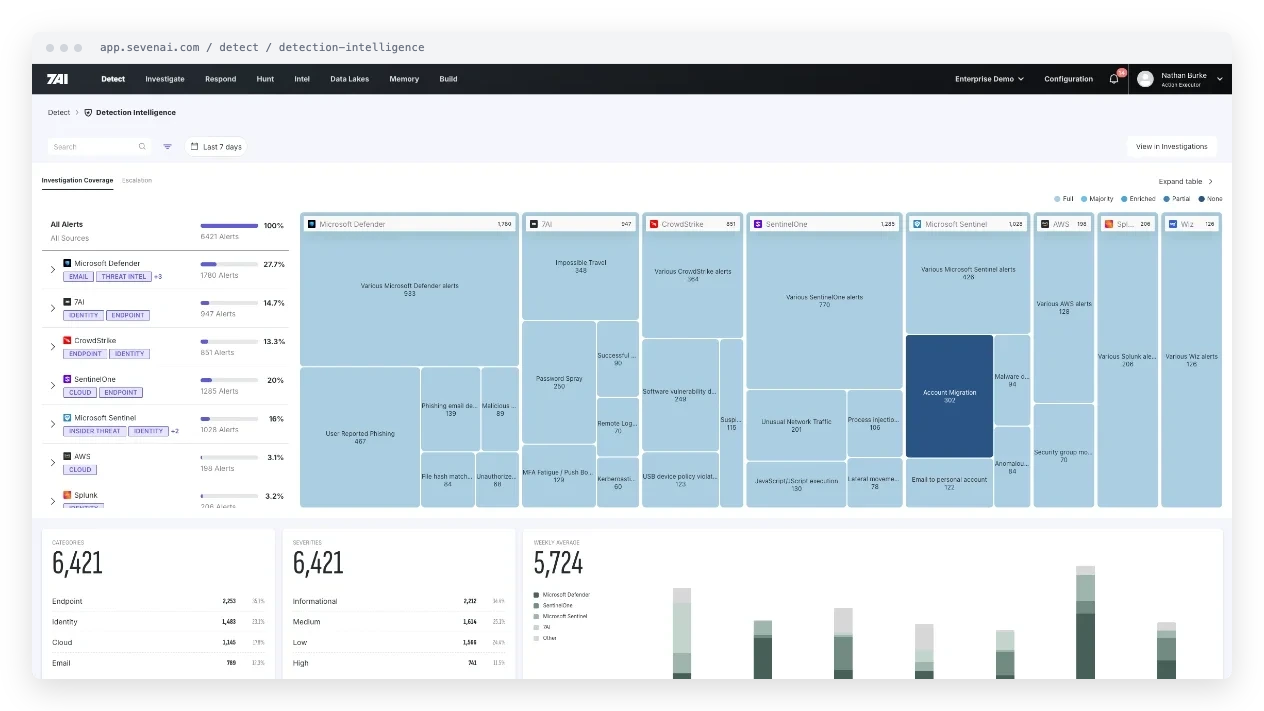
Every alert, every source, one view.
Connect the detection tools you already run across identity, endpoint, cloud, email, and SIEM, and see your entire alert inventory in one place. 7AI shows what each source is producing and how much of it has been investigated to a conclusion.
- Every source connected and normalized into one inventory.
- Investigation coverage shown for each source.
- Nothing sits unseen in a queue.
02 / Detection Coverage
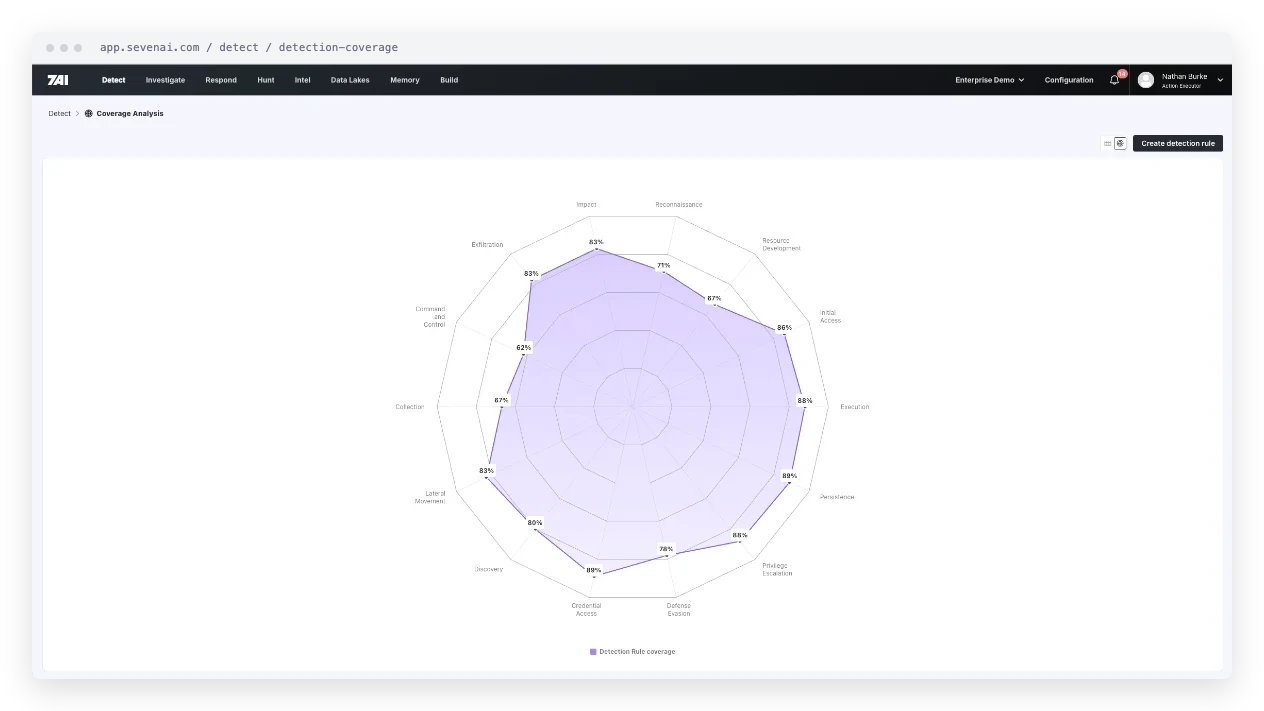
See what you are not catching.
7AI maps your detections to the MITRE ATT&CK techniques attackers actually use, so coverage gaps stop being invisible. Drill into any tactic to see which techniques have no coverage, which are an acceptable risk, and which are handled by an alternative control.
- Coverage scored against known attacker techniques.
- Gaps surfaced tactic by tactic.
- Prioritize what matters for your environment.
03 / Detection Rules
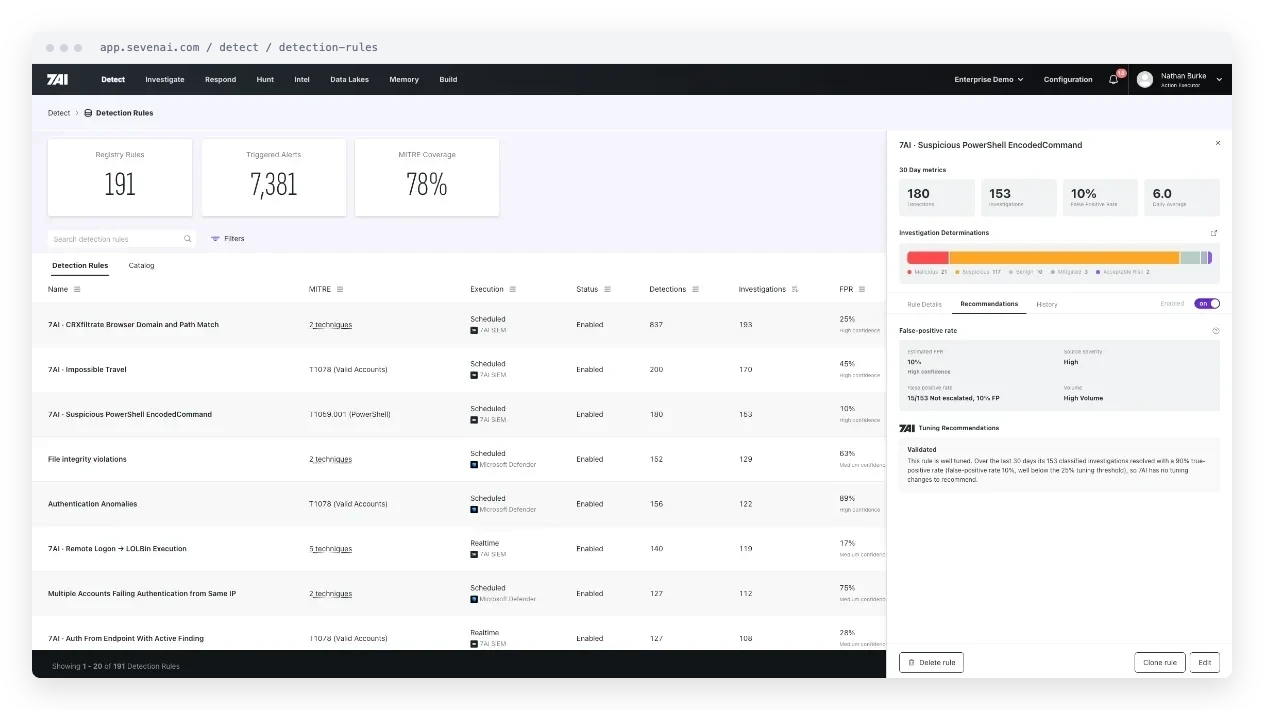
Every rule, and what it is really doing.
All of your detection rules in one inventory, with the techniques they map to, how often they fire, and how many investigations they drive. The rules that earn their place become obvious, and so do the ones that do not.
- One inventory across every connected source.
- Detections and investigations measured per rule.
- Built on the work 7AI already does on every alert.
04 / Recommendations
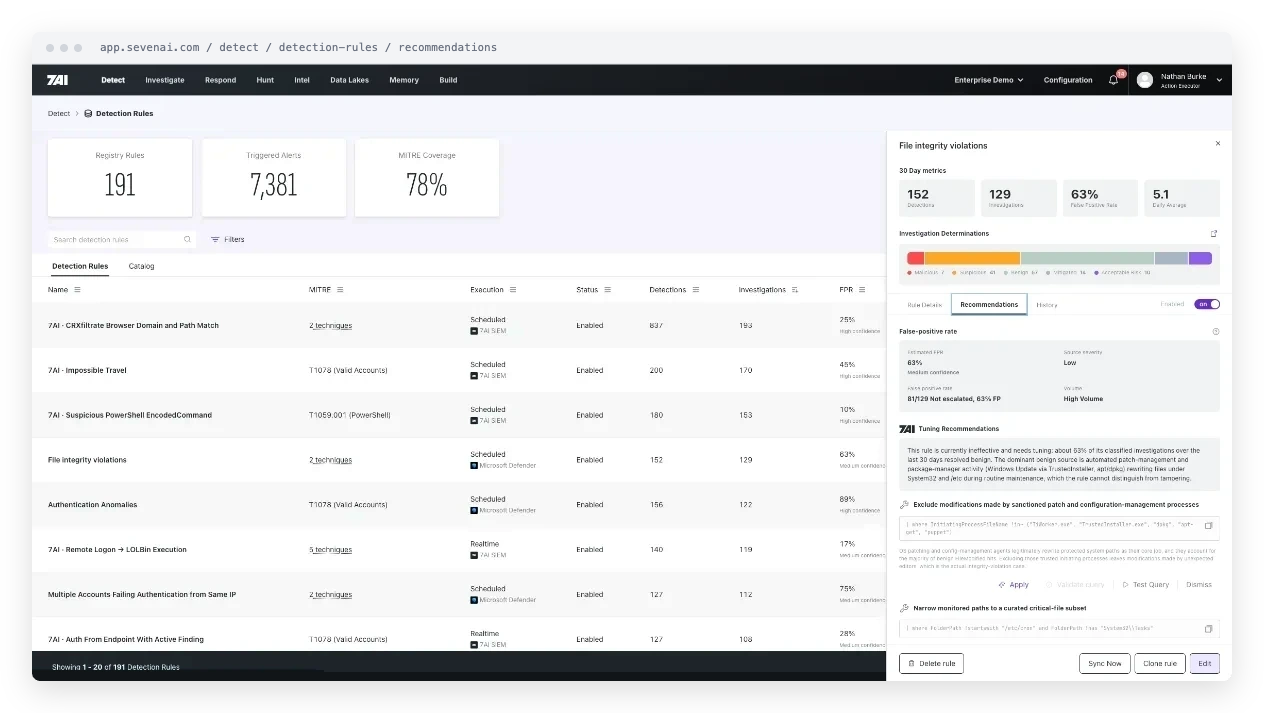
Find the noise. Tune it down.
7AI watches how every rule performs and flags the ones generating false positives at scale. For each one it explains why, quantifies the cost in analyst time, and recommends a precise change scoped to confirmed threat signals, so real detections rise and the noise falls.
- False positive rate measured for every rule.
- A specific, scoped tuning recommendation, not a vague score.
- You stay in control, with humans on the loop.
05 / Detection Routing
Route every detection to the right outcome.
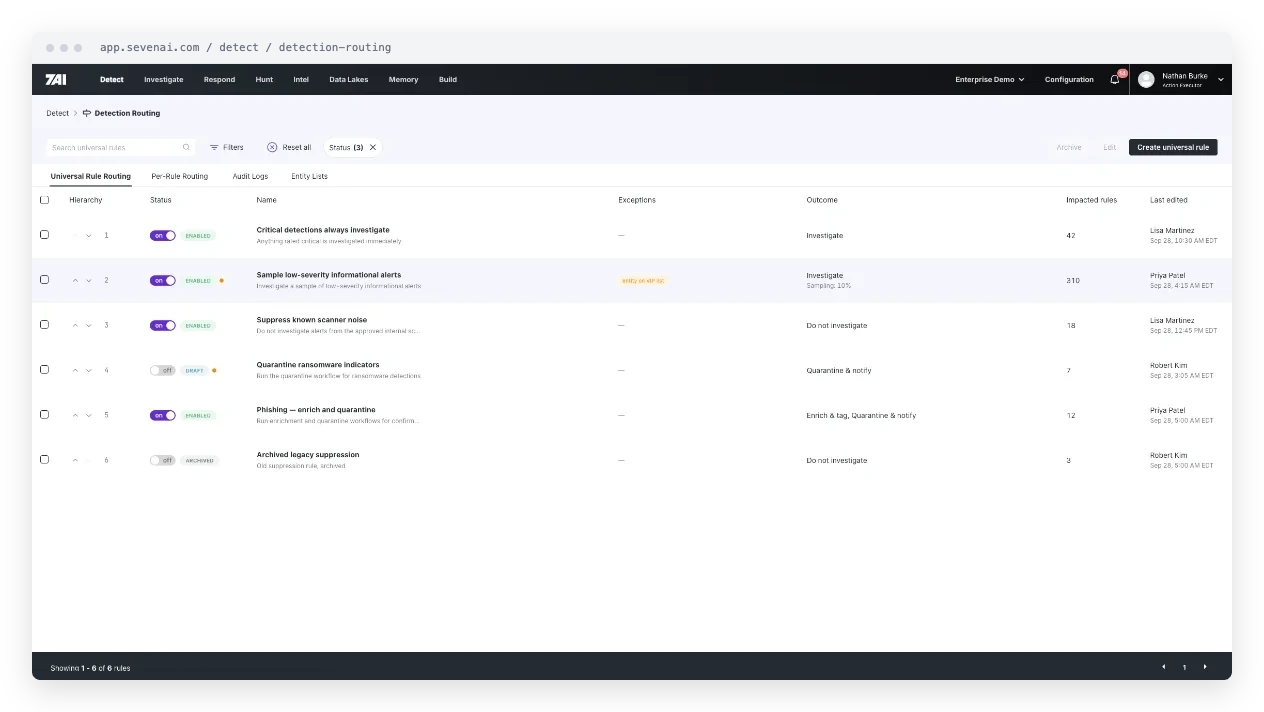
Decide what happens to each detection before it ever reaches a person. Investigate everything critical, sample the low-severity noise, suppress known-good sources, or send confirmed threats straight to enrichment and quarantine. Routing runs continuously, with humans on the loop and a full audit trail.
- Investigate, sample, suppress, or escalate by rule.
- Exceptions for VIPs and known-good sources.
- Every routing decision logged.
A detection layer that gets sharper over time. build what's next.
Questions
Detection optimization, answered.
Take the full tour
See the whole platform, in one guided demo.
A walkthrough of detection intelligence, coverage, rules, and routing, end to end, on a realistic data set. Work on your own detections begins once you are set up.